European Health Data Space Regulation: Key Provisions and Requirements Explained
Sarah Richards, Editorial Team, European Hospital & Healthcare Management
Regulation (EU) 2025/327 establishes the European Health Data Space, the EU’s first sector-specific data framework. This article explains the European Health Data Space regulation: patient rights, EHR system requirements, secondary-use permits, and phased deadlines from 2027. It also outlines the practical EHDS requirements for healthcare organizations preparing for compliance now.
Introduction:
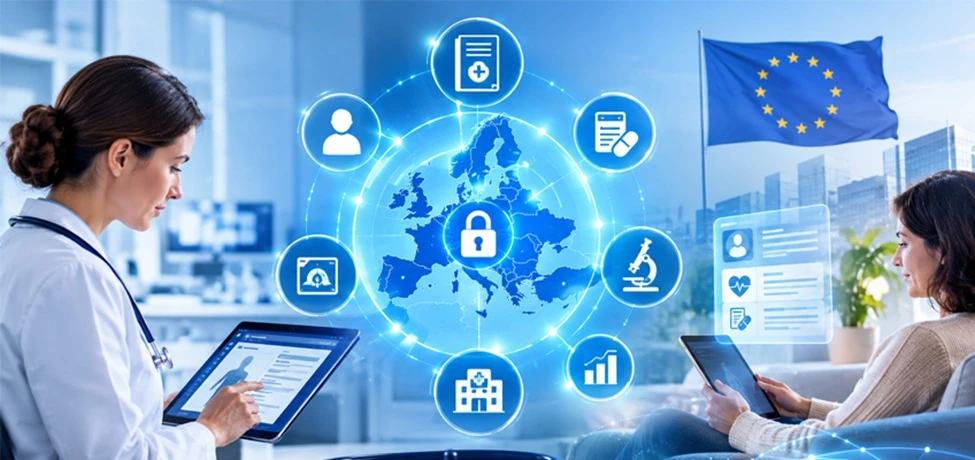
The short answer: The European Health Data Space (EHDS) regulation is Regulation (EU) 2025/327, the EU’s first sector-specific data law. It gives patients control over their electronic health data and sets common rules for the software that holds it. It also creates a controlled route for using health data in research and policy. It applies in stages from March 2027, with the heaviest obligations arriving in 2029 and 2031.
If you work in a hospital, clinic, health-tech company or research team, this law will change how you handle data. Here’s what it says, who it affects and what to do about it.
What is the European Health Data Space regulation?
Picture a patient from Lyon who falls ill in Lisbon. Today, her records are probably stuck in a system the Portuguese doctor can’t read. The EHDS regulation exists to fix that.
Formally, it’s Regulation (EU) 2025/327 of 11 February 2025. It was published in the Official Journal on 5 March 2025 and entered into force later that month. It builds on the GDPR rather than replacing it, adding health-specific rights and obligations on top.
It has three goals:
1. Give people easy, free access to their electronic health data, including across borders.
2. Allow safe reuse of that data for research, innovation, public health and regulation.
3. Create a single EU market for electronic health record (EHR) systems.
EHDS regulation explained: primary use vs. secondary use
Almost everything in the law falls into one of two buckets.
Primary use means using health data to treat the person it belongs to. This covers patient access, sharing records between providers, and e-prescriptions.
Secondary use means using health data for something else, such as medical research, policy planning, statistics, AI development or regulatory work. Think of a researcher studying diabetes outcomes across 15 countries.
Each bucket has its own rules, its own infrastructure and its own timeline.
Key provisions of the EHDS legal framework
1. New rights for individuals
Under the primary-use rules, patients gain the right to:
- see their electronic health data immediately and free of charge
- have it transferred to another provider, including in another Member State
- request corrections
- restrict access for health professionals in some circumstances
Cross-border exchange runs through MyHealth@EU, the EU digital health infrastructure. For patients, that means a doctor abroad can see essentials like a patient summary or ePrescription.
2. Priority data categories
The regulation doesn’t try to digitize everything at once. It starts with priority categories: patient summaries, ePrescriptions, eDispensations, medical images and imaging reports, lab results, and discharge reports. The first group comes first, and the others follow later in the timeline.
3. Rules for EHR systems
This is the part many software vendors underestimate. EHR systems placed on the EU market must meet common requirements for interoperability and logging. Manufacturers must carry out conformity assessment and affix a CE-style marking. The goal is a single market where a system certified in one country works in all of them.
Wellness apps and devices that claim interoperability with EHR systems are pulled in too, so check whether your product falls under the rules.
4. A controlled path for secondary use
Researchers can’t simply request data from any hospital they like. Each Member State must designate Health Data Access Bodies (HDABs). A researcher applies for a data permit, states the purpose, scope and safeguards, and the HDAB approves or refuses. If approved, it tells the data holder to provide the data. Cross-border access runs through HealthData@EU.
The regulation limits what the data can be used for. It also prohibits some uses, such as decisions that harm individuals, like denying insurance, and marketing.
EHDS regulatory requirements: the timeline
|
Date |
What happens |
|
Early 2025 |
Regulation published and in force |
|
26 March 2027 |
General application begins |
|
2029 |
Major primary-use, EHR-system and secondary-use obligations phase in |
|
2031 |
Later data categories (such as imaging, lab results, discharge reports) come in |
|
2035 |
Third countries and international organizations can apply to join HealthData@EU |
Obligations are staggered, so don’t assume one deadline covers everything. Check the date that applies to your data category and role.
EHDS requirements for healthcare organizations
If you’re a hospital, clinic or other provider, a practical checklist looks like this:
- Map your data. Know what electronic health data you hold, where, and in what format. You can’t share or protect what you haven’t inventoried.
- Prepare for patient access. Build or confirm a way for patients to see and export their data without delay or fees.
- Check your EHR vendor. Ask when their product will be EHDS-compliant and how they’ll handle interoperability and logging.
- Plan for data-holder duties. If you’re a data holder, you may have to supply data to an HDAB when a permit is granted. Set up an internal process now.
- Align with the GDPR. The EHDS adds to your existing duties. It doesn’t replace them.
- Train your people. Clinical, IT and legal staff all need to know what’s changing.
The stakes are real. Penalties are set at national level, and data-protection authorities can sanction providers who deny patients their access rights. HDABs can also fine data holders who obstruct secondary use. In serious cases, a data holder can be excluded from participating in the EHDS for up to five years.
Who else is affected?
- EHR and health software manufacturers: conformity and interoperability requirements
- Wellness app and device makers: interoperability claims and data-sharing rules
- Pharma, biotech and researchers: a new route to data, via permits
- Public bodies: designating HDABs and digital health authorities
Common questions about the EHDS regulation
Does the EHDS replace the GDPR?
No. It specifies and complements the GDPR’s rights for electronic health data.
When does the EHDS apply?
General application starts on 26 March 2027. Many obligations phase in later, in 2029 and 2031.
Is the EHDS a regulation or a directive?
A regulation. It applies directly across Member States without national transposition, though countries must set up authorities and penalties.
Do patients have to share their data for research?
Secondary-use rules are set out in the regulation, including safeguards and opt-out provisions in many cases. Check the Member State’s implementation for exact details.
What is a Health Data Access Body?
A national authority that reviews requests for secondary use of health data and grants or refuses permits.
Final thoughts
The EHDS regulation is a big shift, but a staged one, and organizations that start early will have an easier time. Begin with a data map, ask your vendors the awkward questions now, and watch for national implementing rules in your country.
If you’re building your compliance plan, bookmark the Commission’s official EHDS page, since implementing acts will keep arriving over the next few years.
Sarah Richards, a member of the Editorial Team at European Hospital & Healthcare Management, uses her extensive background in healthcare communication to create clear and engaging content. With a strong commitment to making complex healthcare topics accessible, Sarah helps the team achieve its goal of delivering timely and impactful information to the global healthcare community.